

-
Corporate
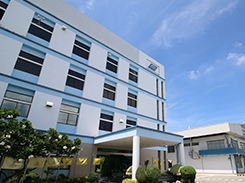 Thai Parkerizing is a leader in Heat & Surface treatment business.
-
Chemical Products
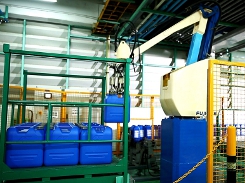 Surface treatment chemicals for a diverse range of purposes with our extensive technical supports.
-
Processing Services
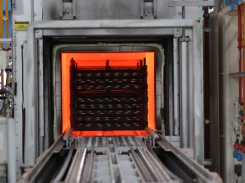 Various kind of heat and surface treatment services to fulfill customer requirements with high quality systems.
-
Laboratory Services
 Thai Parkerizing Analysis Center is an analysis and testing laboratory in chemical, metallurgical and environmental fields.
- Articles
- Contact us

Privacy Policy


Announcement
Personal Data Protection Policy and Guidelines
Thai Parkerizing Co., Ltd. (the "Company") recognizes the utmost importance of maintaining the security and confidentiality of personal data belonging to all customers, business partners, and visitors. To ensure that the collection, use, disclosure, transfer, and enforcement of the rights of customers, business partners, or visitors are strictly conducted with maximum security, the Company hereby establishes this Personal Data Protection Policy and Guidelines in compliance with the Personal Data Protection Act B.E. 2562 (2019) (PDPA) as follows:
- Scope of Enforcement
- This Announcement shall apply to all Data Subjects, including customers, business partners, visitors, and any other individuals whose personal data is collected, used, and disclosed by the Company.
- This Announcement shall apply to all operational activities of the Company involving personal data of customers, business partners, or visitors, including data collection channels, types and formats of stored data, business purposes for data usage, data sharing or cross-border transfer, and disclosure to statutory regulatory authorities.
- This Announcement covers personal data received or collected through website visits, product/service purchases, membership registration, feedback, complaints, or other necessary activities via the Company's website, mobile applications, social media channels, and authorized distributors. However, it does not cover third-party websites, applications, or social media channels linked to the Company's platform, nor does it apply to stores not managed by the Company.
- Definitions
"Company" means Thai Parkerizing Co., Ltd.
"Data Controller" means the Company, having the authority and responsibility to make decisions regarding the collection, use, or disclosure of personal data of customers, business partners, or visitors, including authorized designees acting on behalf of the Company.
"Data Processor" means an individual or legal entity that processes the collection, use, or disclosure of personal data pursuant to the instructions or on behalf of the Company.
"Data Subject" refers to:
Customer: An individual who purchases products or uses services of the Company.
Business Partner (Supplier): A company, partnership, shop, or individual that sells or provides goods or services to the Company.
Visitor: An external person who enters Company premises to contact business, visit, inspect activities, or perform duties other than commercial transactions, including online website visitors and registered members (if any).
"Personal Data" means any information relating to an individual which enables the identification of such individual, whether directly or indirectly, but excluding information of deceased persons.
"Website" means www.thaiparker.co.th
Categories of identifiable Personal Data collected and protected under this Policy:
- Personal Identification Details: First name - last name, gender, date of birth, national ID card number, passport number, tax identification number, nationality, etc.
- Contact Details: Telephone number, email address, current residential address, ID address, billing/tax invoice address, shipping/delivery address, etc.
- Financial Details: Payment channels, credit/debit card information, bank account details, etc.
- Transaction Details: Payment records, purchase history of goods/services, warranty records, complaints, and related transaction details.
- Membership Details: Member ID, membership tier, duration, and transaction history.
- Behavioral Details: Purchasing behavior across channels, customer satisfaction feedback, electronic withholding tax requests, and Cookie tracking data.
- Sensitive Personal Data: Race, religion, biometric data (fingerprints, facial recognition), genetic data, and other sensitive attributes required for legitimate processing.
- Collection, Use, and Disclosure of Personal Data
- The Company respects the privacy rights of Data Subjects to the highest standard.
- Personal data shall be collected, retained, and processed strictly to the extent necessary for legitimate business operations, legal obligations, or regulatory requirements.
- Personal data shall be collected directly from Data Subjects. Data obtained from third-party sources will not be processed without explicit consent unless authorized by law.
- Collection of various data categories is conducted strictly for explicit business objectives.
- Clear roles for data collectors, processors, custodians, users, and approvers shall be established, accompanied by auditing procedures to maintain confidentiality as mandated by law.
- Data disclosure to government bodies or external auditors (e.g., financial or quality auditors) shall be executed with strict confidentiality protocols and audit logs.
- Personal data retained by the Company is treated as vital commercial assets. Unauthorized access, disclosure, or destruction will be penalized to the maximum extent under the law.
- Robust security control measures shall be maintained to safeguard data collection, processing, and disclosure.
- Personal data may be processed for Company activities such as CSR projects, PR media, training sessions, or corporate events aligned with legitimate business purposes.
- Contact details shall be utilized for business communications, service updates, promotional campaigns, privileges (based on consent), delivery logistics, and essential operational inquiries.
- Financial and transaction details shall be processed for commercial payment administration.
- Behavioral details shall be processed for website analytics, market research, consumer preference evaluations, surveys, and statistical planning for corporate development.
- Access, Inspection, Rectification, Consent Withdrawal, and Erasure
- Data Subjects reserve the right to request access to their stored personal data in accordance with prescribed procedures.
- Data Subjects shall furnish necessary documents or personal data upon request within specified timeframes for business performance.
- Data Subjects are required to maintain up-to-date details (e.g., name, tax ID, legal address) by notifying the Company within 30 days of any alteration.
- Data Subjects may request consent withdrawal or data destruction upon termination of business relations, subject to legal retention exceptions for legal claims or statutory compliance.
-
Data Processing Responsibilities and Adjustments
Department managers directly interacting with Data Subjects shall execute the following:
- Inform Data Subjects of the purpose, scope, rights, and duties outlined in this Policy.
- Manage data in good faith and strict confidence. Any modifications or additions must be submitted through designated managers; unauthorized alterations are strictly forbidden.
- Promptly notify Data Subjects upon re-assignment, replacement, or resignation of handling personnel to prevent impersonation, misuse, or unauthorized breach.
- Maintain comprehensive data processing audit logs to ensure full regulatory compliance.
- Governance and Governance Roles
As the statutory Data Controller, the Company establishes employee operational duties as follows:
- Appoint a Personal Data Protection Working Committee comprising department managers/supervisors and a Data Protection Officer (DPO) (if applicable) to oversee regulatory compliance.
- Review and authorize new data processing channels, cross-border transfers, or activities beyond standard delegation limits.
- Conduct annual reviews (at minimum) of data collection, storage, and processing security measures.
- Designate emergency incident commanders to manage data leaks or security breaches.
- Cross-Border Data Transfer
- Personal data transfers to foreign jurisdictions or international organizations shall occur only if the recipient country maintains adequate data protection standards equivalent to applicable laws.
- Personal data may be shared with parent companies, subsidiaries, affiliated entities, or business partners to enhance service standards and operational performance.
- Data Security Standards
- Standardized security controls are deployed to prevent unauthorized access, destruction, loss, alteration, or disclosure.
- Security protocols shall undergo annual evaluation to ensure structural integrity and legal compliance.
- The Company shall assume liability for damages directly resulting from its security failures, excluding damages caused by Data Subject negligence (e.g., failure to log out from Company portals) or third-party authorizations granted directly by the Data Subject.
- Periodic risk evaluations of data protection systems shall be conducted strictly for business operational security.
- Data Breach Notification
In the event of a security breach compromising personal data or resulting in public leakage, the Company shall promptly notify affected Data Subjects alongside remedial action plans for high-risk cases.
- Data Retention and Destruction
Personal data shall be securely erased, destroyed, or permanently anonymized within a reasonable period when:
- The data is no longer necessary for its original collected purpose.
- Retention is no longer required under statutory mandates or corporate business necessity.
- Violations and Disciplinary Penalties
- Any employee who unauthorizedly collects, uses, discloses, breaches, or misuses personal data for private gain shall be deemed to have committed gross breach of trust and willful misconduct, subject to immediate termination without severance compensation.
- Designated Data Controllers/Processors who violate provisions shall face enhanced disciplinary penalties compared to general staff.
- Non-compliant employees causing financial or reputational damage shall be personally liable for full compensation under applicable civil and criminal laws.
- Contact and Inquiries
Customers, suppliers, or visitors who wish to contact or complain about management of Personal Data may contact the company at No. 570 Moo.4, Bangpoo Industrial Estate, Soi.12B, Prakasa, Muang, Samutprakan 10280 by addressing Ms.Pattana Kaewkiriya, Human Resources Department or call 02-324-6600 ext. 6122 or email: kritsana@thaiparker.co.th The company shall investigate and find the best solutions to the complained issued promptly and fairly.
The company are instructed to strictly comply with this Policy to ensure personal data is collected, used, and disclosed securely in compliance with privacy laws.
- This Announcement shall apply to all Data Subjects, including customers, business partners, visitors, and any other individuals whose personal data is collected, used, and disclosed by the Company.
- This Announcement shall apply to all operational activities of the Company involving personal data of customers, business partners, or visitors, including data collection channels, types and formats of stored data, business purposes for data usage, data sharing or cross-border transfer, and disclosure to statutory regulatory authorities.
- This Announcement covers personal data received or collected through website visits, product/service purchases, membership registration, feedback, complaints, or other necessary activities via the Company's website, mobile applications, social media channels, and authorized distributors. However, it does not cover third-party websites, applications, or social media channels linked to the Company's platform, nor does it apply to stores not managed by the Company.
"Company" means Thai Parkerizing Co., Ltd.
"Data Controller" means the Company, having the authority and responsibility to make decisions regarding the collection, use, or disclosure of personal data of customers, business partners, or visitors, including authorized designees acting on behalf of the Company.
"Data Processor" means an individual or legal entity that processes the collection, use, or disclosure of personal data pursuant to the instructions or on behalf of the Company.
"Data Subject" refers to:
Customer: An individual who purchases products or uses services of the Company.
Business Partner (Supplier): A company, partnership, shop, or individual that sells or provides goods or services to the Company.
Visitor: An external person who enters Company premises to contact business, visit, inspect activities, or perform duties other than commercial transactions, including online website visitors and registered members (if any).
"Personal Data" means any information relating to an individual which enables the identification of such individual, whether directly or indirectly, but excluding information of deceased persons.
"Website" means www.thaiparker.co.th
Categories of identifiable Personal Data collected and protected under this Policy:
- Personal Identification Details: First name - last name, gender, date of birth, national ID card number, passport number, tax identification number, nationality, etc.
- Contact Details: Telephone number, email address, current residential address, ID address, billing/tax invoice address, shipping/delivery address, etc.
- Financial Details: Payment channels, credit/debit card information, bank account details, etc.
- Transaction Details: Payment records, purchase history of goods/services, warranty records, complaints, and related transaction details.
- Membership Details: Member ID, membership tier, duration, and transaction history.
- Behavioral Details: Purchasing behavior across channels, customer satisfaction feedback, electronic withholding tax requests, and Cookie tracking data.
- Sensitive Personal Data: Race, religion, biometric data (fingerprints, facial recognition), genetic data, and other sensitive attributes required for legitimate processing.
- The Company respects the privacy rights of Data Subjects to the highest standard.
- Personal data shall be collected, retained, and processed strictly to the extent necessary for legitimate business operations, legal obligations, or regulatory requirements.
- Personal data shall be collected directly from Data Subjects. Data obtained from third-party sources will not be processed without explicit consent unless authorized by law.
- Collection of various data categories is conducted strictly for explicit business objectives.
- Clear roles for data collectors, processors, custodians, users, and approvers shall be established, accompanied by auditing procedures to maintain confidentiality as mandated by law.
- Data disclosure to government bodies or external auditors (e.g., financial or quality auditors) shall be executed with strict confidentiality protocols and audit logs.
- Personal data retained by the Company is treated as vital commercial assets. Unauthorized access, disclosure, or destruction will be penalized to the maximum extent under the law.
- Robust security control measures shall be maintained to safeguard data collection, processing, and disclosure.
- Personal data may be processed for Company activities such as CSR projects, PR media, training sessions, or corporate events aligned with legitimate business purposes.
- Contact details shall be utilized for business communications, service updates, promotional campaigns, privileges (based on consent), delivery logistics, and essential operational inquiries.
- Financial and transaction details shall be processed for commercial payment administration.
- Behavioral details shall be processed for website analytics, market research, consumer preference evaluations, surveys, and statistical planning for corporate development.
- Data Subjects reserve the right to request access to their stored personal data in accordance with prescribed procedures.
- Data Subjects shall furnish necessary documents or personal data upon request within specified timeframes for business performance.
- Data Subjects are required to maintain up-to-date details (e.g., name, tax ID, legal address) by notifying the Company within 30 days of any alteration.
- Data Subjects may request consent withdrawal or data destruction upon termination of business relations, subject to legal retention exceptions for legal claims or statutory compliance.
Department managers directly interacting with Data Subjects shall execute the following:
- Inform Data Subjects of the purpose, scope, rights, and duties outlined in this Policy.
- Manage data in good faith and strict confidence. Any modifications or additions must be submitted through designated managers; unauthorized alterations are strictly forbidden.
- Promptly notify Data Subjects upon re-assignment, replacement, or resignation of handling personnel to prevent impersonation, misuse, or unauthorized breach.
- Maintain comprehensive data processing audit logs to ensure full regulatory compliance.
As the statutory Data Controller, the Company establishes employee operational duties as follows:
- Appoint a Personal Data Protection Working Committee comprising department managers/supervisors and a Data Protection Officer (DPO) (if applicable) to oversee regulatory compliance.
- Review and authorize new data processing channels, cross-border transfers, or activities beyond standard delegation limits.
- Conduct annual reviews (at minimum) of data collection, storage, and processing security measures.
- Designate emergency incident commanders to manage data leaks or security breaches.
- Personal data transfers to foreign jurisdictions or international organizations shall occur only if the recipient country maintains adequate data protection standards equivalent to applicable laws.
- Personal data may be shared with parent companies, subsidiaries, affiliated entities, or business partners to enhance service standards and operational performance.
- Standardized security controls are deployed to prevent unauthorized access, destruction, loss, alteration, or disclosure.
- Security protocols shall undergo annual evaluation to ensure structural integrity and legal compliance.
- The Company shall assume liability for damages directly resulting from its security failures, excluding damages caused by Data Subject negligence (e.g., failure to log out from Company portals) or third-party authorizations granted directly by the Data Subject.
- Periodic risk evaluations of data protection systems shall be conducted strictly for business operational security.
In the event of a security breach compromising personal data or resulting in public leakage, the Company shall promptly notify affected Data Subjects alongside remedial action plans for high-risk cases.
Personal data shall be securely erased, destroyed, or permanently anonymized within a reasonable period when:
- The data is no longer necessary for its original collected purpose.
- Retention is no longer required under statutory mandates or corporate business necessity.
- Any employee who unauthorizedly collects, uses, discloses, breaches, or misuses personal data for private gain shall be deemed to have committed gross breach of trust and willful misconduct, subject to immediate termination without severance compensation.
- Designated Data Controllers/Processors who violate provisions shall face enhanced disciplinary penalties compared to general staff.
- Non-compliant employees causing financial or reputational damage shall be personally liable for full compensation under applicable civil and criminal laws.
Customers, suppliers, or visitors who wish to contact or complain about management of Personal Data may contact the company at No. 570 Moo.4, Bangpoo Industrial Estate, Soi.12B, Prakasa, Muang, Samutprakan 10280 by addressing Ms.Pattana Kaewkiriya, Human Resources Department or call 02-324-6600 ext. 6122 or email: kritsana@thaiparker.co.th The company shall investigate and find the best solutions to the complained issued promptly and fairly.
The company are instructed to strictly comply with this Policy to ensure personal data is collected, used, and disclosed securely in compliance with privacy laws.


